
| CompTIA A+ |
Lesson 6: Security ConceptsSommaire
Topic A: Logical Security ConceptsObjectifs de la Sécurité informatiqueObjectifs principauxLa sécurité informatique vise généralement cinq principaux objectifs :
la préventionLe plus souvent, prévenir le risque informatique se résume en cinq points
la détectionMalgré toutes les mesures de prévention, aucun système informatique n'est infaillible. D’où l’intérêt de mettre en place un système de détection fiable et performant. La détection suppose un suivi attentif et constant de l’état des systèmes notamment grâce à la diffusion d’alertes automatiques.la réactionBien réagir en cas d’incident c’est réagir vite et de manière ordonnée.Topic B: Threats and VulnerabilitiesThreats
Les attaques informatiques de type Social Engineering
Cyber CriminalsIn the early years of the cybersecurity world, the typical cyber criminals were teenagers or hobbyists operating from a home PC, with attacks mostly limited to pranks and vandalism. Today, the world of the cyber criminals has become more dangerous. Attackers are individuals or groups who attempt to exploit vulnerabilities for personal or financial gain. Cyber criminals are interested in everything from credit cards to product designs, and anything with value.
AmateursAmateurs, or script kiddies, have little or no skill, often using existing tools or instructions found on the Internet to launch attacks. Some are just curious, while others try to demonstrate their skills and cause harm. They may be using basic tools, but the results can still be devastating. HackersThis group of criminals breaks into computers or networks to gain access for various reasons. The intent of the break-in determines the classification of these attackers as white, gray, or black hats. - White hat attackers break into networks or computer systems to discover weaknesses in order to improve the security of these systems. The owners of the system give permission to perform the break-in, and they receive the results of the test. - Black hat attackers take advantage of any vulnerability for illegal personal, financial or political gain. Gray hat attackers are somewhere between white and black hat attackers. - The gray hat attackers may find a vulnerability and report it to the owners of the system if that action coincides with their agenda. Some gray hat hackers publish the facts about the vulnerability on the Internet, so that other attackers can exploit it. Organized HackersThese criminals include organizations of cyber criminals, hacktivists, terrorists, and state-sponsored hackers. Cyber criminals are usually groups of professional criminals focused on control, power, and wealth. The criminals are highly sophisticated and organized, and may even provide cybercrime as a service. Hacktivists make political statements to create awareness to issues that are important to them. Hacktivists publically publish embarrassing information about their victims. State-sponsored attackers gather intelligence or commit sabotage on behalf of their government. These attackers are usually highly trained and well-funded. Their attacks focus on specific goals that are beneficial to their government. Some state-sponsored attackers are even members of their nations’ armed forces. Cyber Criminal MotivesCyber criminal profiles and motives have changed over the years. Hacking started in the ‘60s with phone freaking (or phreaking) which refers to using various audio frequencies to manipulate phone systems. In the mid-‘80s, criminals used computer dial-up modems to connect computers to networks and used password-cracking programs to gain access to data. Nowadays, criminals are going beyond just stealing information. Criminals can now use malware and viruses as high tech weapons. However, the greatest motivation for most cyber criminals is financial. Cybercrime has become more lucrative than the illegal drug trade.People who, for purposes of larceny or to amuse themselves, like to break into computers — they’re called crackers — are a clever bunch.If there is a vulnerability in a system, they will find it. CybersécuritéCybersecurity is a general term to describe an industry where professionals manage security risks secure and defend infrastructures, systems, and applications that may be internet-associated. Les professionnels de la cybersécurité doivent avoir les mêmes compétences que les agresseurs informatiques. Cependant, ils doivent travailler dans le cadre de la législation locale, nationale et internationale. Les professionnels de la cybersécurité doivent également faire preuve d’éthique. La cybersécurité consiste en l’effort continu pour protéger les systèmes mis en réseau et les données contre l’utilisation ou le méfait non autorisés. ■ À titre personnel, vous devez protéger votre identité, vos données et vos périphériques informatiques.■ Au niveau de l’entreprise, tout le monde est responsable de la protection de la réputation, des données et des clients de l’entreprise. ■ Au niveau national, la sécurité nationale, ainsi que la sécurité et le bien-être des citoyens sont en jeu. Votre identité en ligne et offlineComme vous passez plus de temps en ligne, votre identité, en ligne et offline, peut affecter votre vie. Votre identité offline est la personne avec qui vos amis et votre famille interagissent au quotidien à la maison, à l’école ou au travail. Ils connaissent vos informations personnelles comme votre nom, votre âge ou votre adresse. Votre identité en ligne représente qui vous êtes dans le cyberespace. Votre identité en ligne traduit votre manière de vous présenter aux autres en ligne. Cette identité en ligne doit uniquement révéler une quantité limitée d’informations vous concernant. Vous devez faire attention lorsque vous choisissez un nom d’utilisateur ou un pseudonyme pour votre identité en ligne. Le nom d’utilisateur ne doit pas inclure d'informations personnelles. Il doit être adéquat et respectueux. Ce nom d’utilisateur ne doit pas pousser les inconnus à penser que vous êtes une cible facile pour la cybercriminalité ou pour une attention indésirable. World CyberAttacks livehttps://threatmap.checkpoint.com/ThreatPortal/livemap.htmlTopic C: Physical Security MeasuresTypical physical security includes door locks, cipher locks, keys, guards, and fences, but physical security regarding computers can mean much more. Companies commonly use electronic key cards, instead of keys, for physical access to rooms. Electronic key cards are part of an access control system, which includes the key cards, door readers, and software to control and monitor the system. 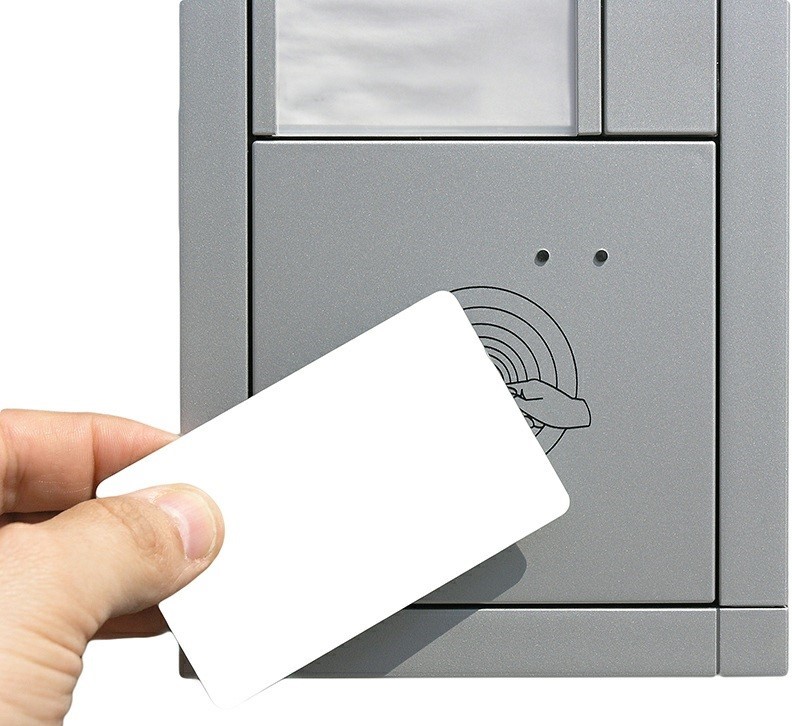 Electronic key cards have many benefits, including the following:
|
